Blog
Hands-on frontend and JavaScript writing: React and Next.js, modern CSS, npm and supply-chain security, and what JavaScript runtimes actually do under the hood.
6 postsRSS feed
TanStack npm Supply Chain Attack: What Happened and How to Protect Your Projects
TanStack packages were compromised in a mass npm supply chain attack. Here's a deep-dive into what happened, how the attack worked, and the concrete steps every JavaScript developer must take to protect their projects right now.
5 min read
Earlier posts
Minimum Release Age: npm, pnpm, Yarn, Bun and Deno Settings
Fix npm's “min-release-age is not a valid npm option” error, then set the same cooldown in pnpm, Yarn, Bun and Deno: copy-paste config, units and versions.
npm RFC: Making Install Scripts Opt-In — A Deep Dive into What It Means for JavaScript Security
A landmark npm RFC proposes making install scripts opt-in by default. This deep-dive covers how the current system works, why it's dangerous, what the RFC proposes, the tradeoffs involved, and how you can protect yourself right now.
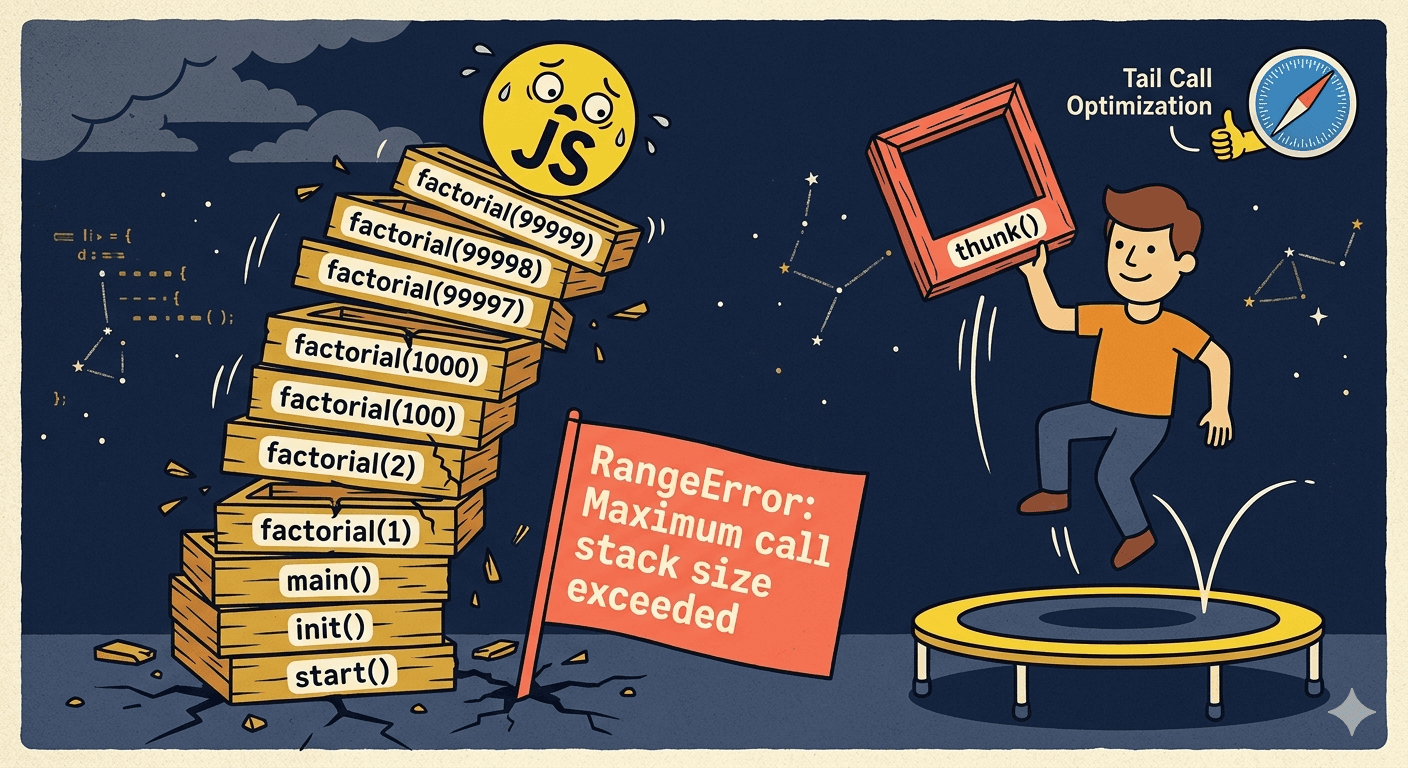
Proper Tail Calls in JavaScript: Why Only Safari Supports Them
Proper tail calls (ES2015) only work in Safari and Bun, which run on JavaScriptCore. Chrome, Node.js, Deno and Firefox never shipped them. Support table and fixes.
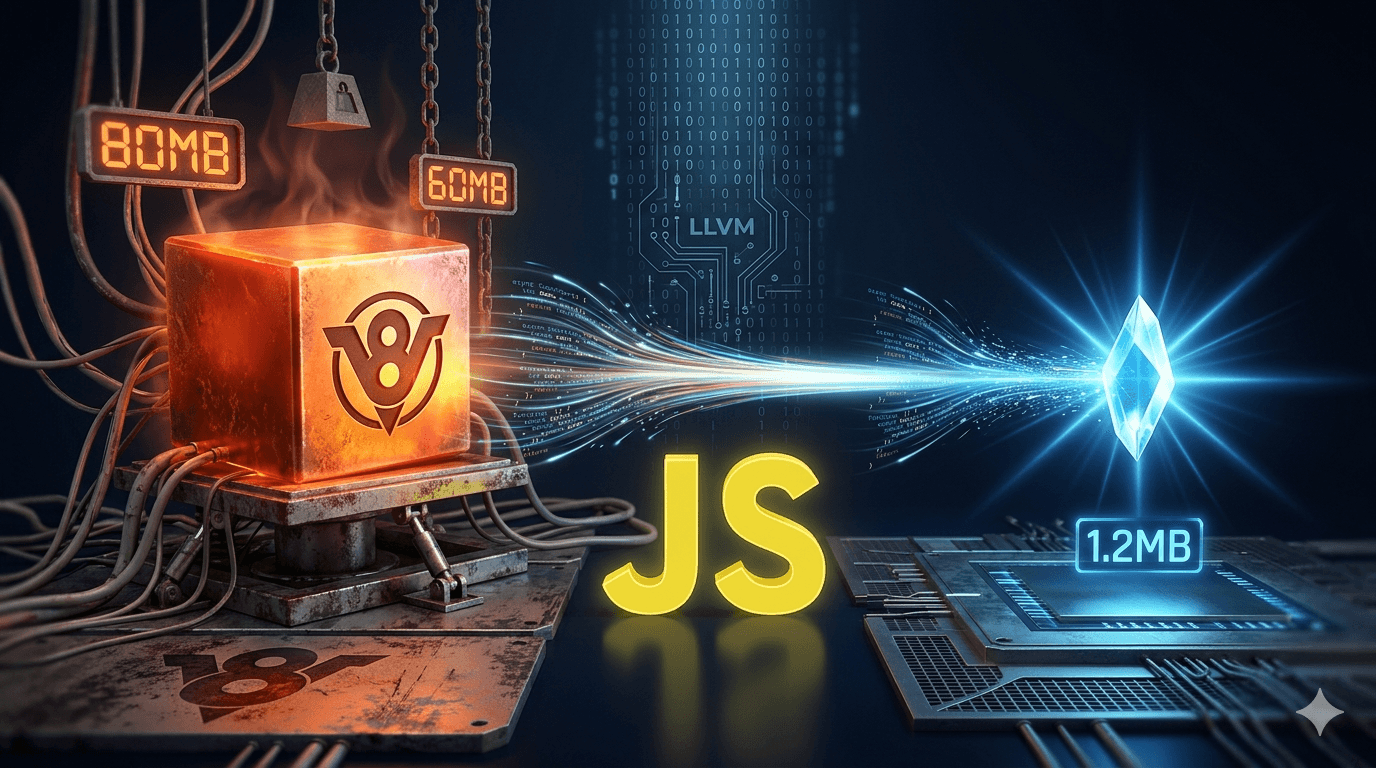
BlueJS: Compiling JavaScript to 1.2MB Native Binaries Without V8
BlueJS is a groundbreaking new compiler that turns JavaScript into tiny native binaries without bundling V8. We explore how it works, what it's good for, and where it fits in the future of JavaScript deployment.
Building My Portfolio with Next.js 15 — What I Learned
Every developer rewrites their portfolio eventually. Here's the stack I chose, what surprised me about Next.js 15's App Router, and a few things I'd do differently.